Updates from VeilNet
News, explainers and milestones from the VeilNet team.
All 12 posts
Sandboxing AI agents by what they can reach
An AI agent is only as dangerous as what it can reach. Containers share the host's kernel and its networks, and a VM per agent is strong but heavy. Here's a third way: give every agent its own compartment on VeilNet, so it reaches its own tools, and the internet only through an exit you run.
The supermarket fridge attacks: what if the controllers had been on VeilNet?
Attackers warmed up supermarket fridges across Europe through controllers that anyone on the internet could reach. The makers and Europe's cyber agencies now agree on the fix: take them off the internet. So what if those controllers had been connected through VeilNet? Here's what the attackers would have found, and why it would have been simpler to roll out than a VPN at every store.
One address, many servers: load balancing without a load balancer
Spreading a service across several servers usually means DNS round robin or a load balancer in the middle. VeilNet does it with one shared address: each client picks a server for itself, stays on it, and moves within seconds if that server goes away. Here's how it works, and where it fits.
Multi-cloud Kubernetes, without a VPN gateway in every cloud
Running Kubernetes across clouds usually means a VPN gateway in each, a tunnel between every pair and route tables to keep in step. Here's why a mesh VPN like Tailscale struggles with it, and a simpler way: join every node to VeilNet and run the cluster on VeilNet's interface, so nodes in every cloud share one flat, post-quantum network.
Silent to strangers: defending against the zero-day nobody has found yet
Nobody can patch a flaw that hasn't been found yet. What you can control is who gets to talk to your software before they've proved who they are. Here's why every reply to a stranger is a risk, how VeilNet's knock keeps your services silent until a member proves itself, and where that silence stops.
You can't migrate what you can't see: finding your quantum risk with a CBOM
Every organisation has to move off quantum-vulnerable cryptography, and most can't yet say where it's in use. Here's why the answer lives in your traffic rather than your spreadsheets, how VeilNet's observer reads it without touching it, and how that becomes a cryptography bill of materials and a migration plan.
Tailworm: when the agent that secures your network becomes the way in
On Sunday, a researcher showed how one compromised laptop with an SSH grant could take root on a server in a Tailscale network, and then on the next one. Tailscale is fixing it fast. The lesson goes well past one product, though. The agents we install to secure access now hold some of the most powerful positions on our machines. Here's what went wrong, what we can learn from it, how VeilNet is designed to avoid it, and how to move across.
How Shor's algorithm actually breaks RSA
Most explanations stop at qubits being 0 and 1 at once, which tells you very little. Here we build a tiny RSA key on a clock of 15 and break it by hand with Shor's algorithm: an ordinary piece of arithmetic called the oracle, a hidden rhythm, and a Fourier transform that loads the dice in favour of the answer.
After eMudhra: a post-quantum PKI tree with your organisation at the root
In October, eight certificate authority keys trusted by every major browser turned out to be guessable. Here's how the web's chain of trust works, why one weak link puts everyone at risk, and how VeilNet's post-quantum PKI tree puts every organisation at the root of its own.
Taking sovereign post-quantum networking to Europe with Austrade
VeilNet has been selected for Austrade's Quantum Mission Europe. From 26 October to 6 November we're meeting customers, investors and governments across five of Europe's major quantum markets, finishing at the UK National Quantum Technologies Showcase in London.
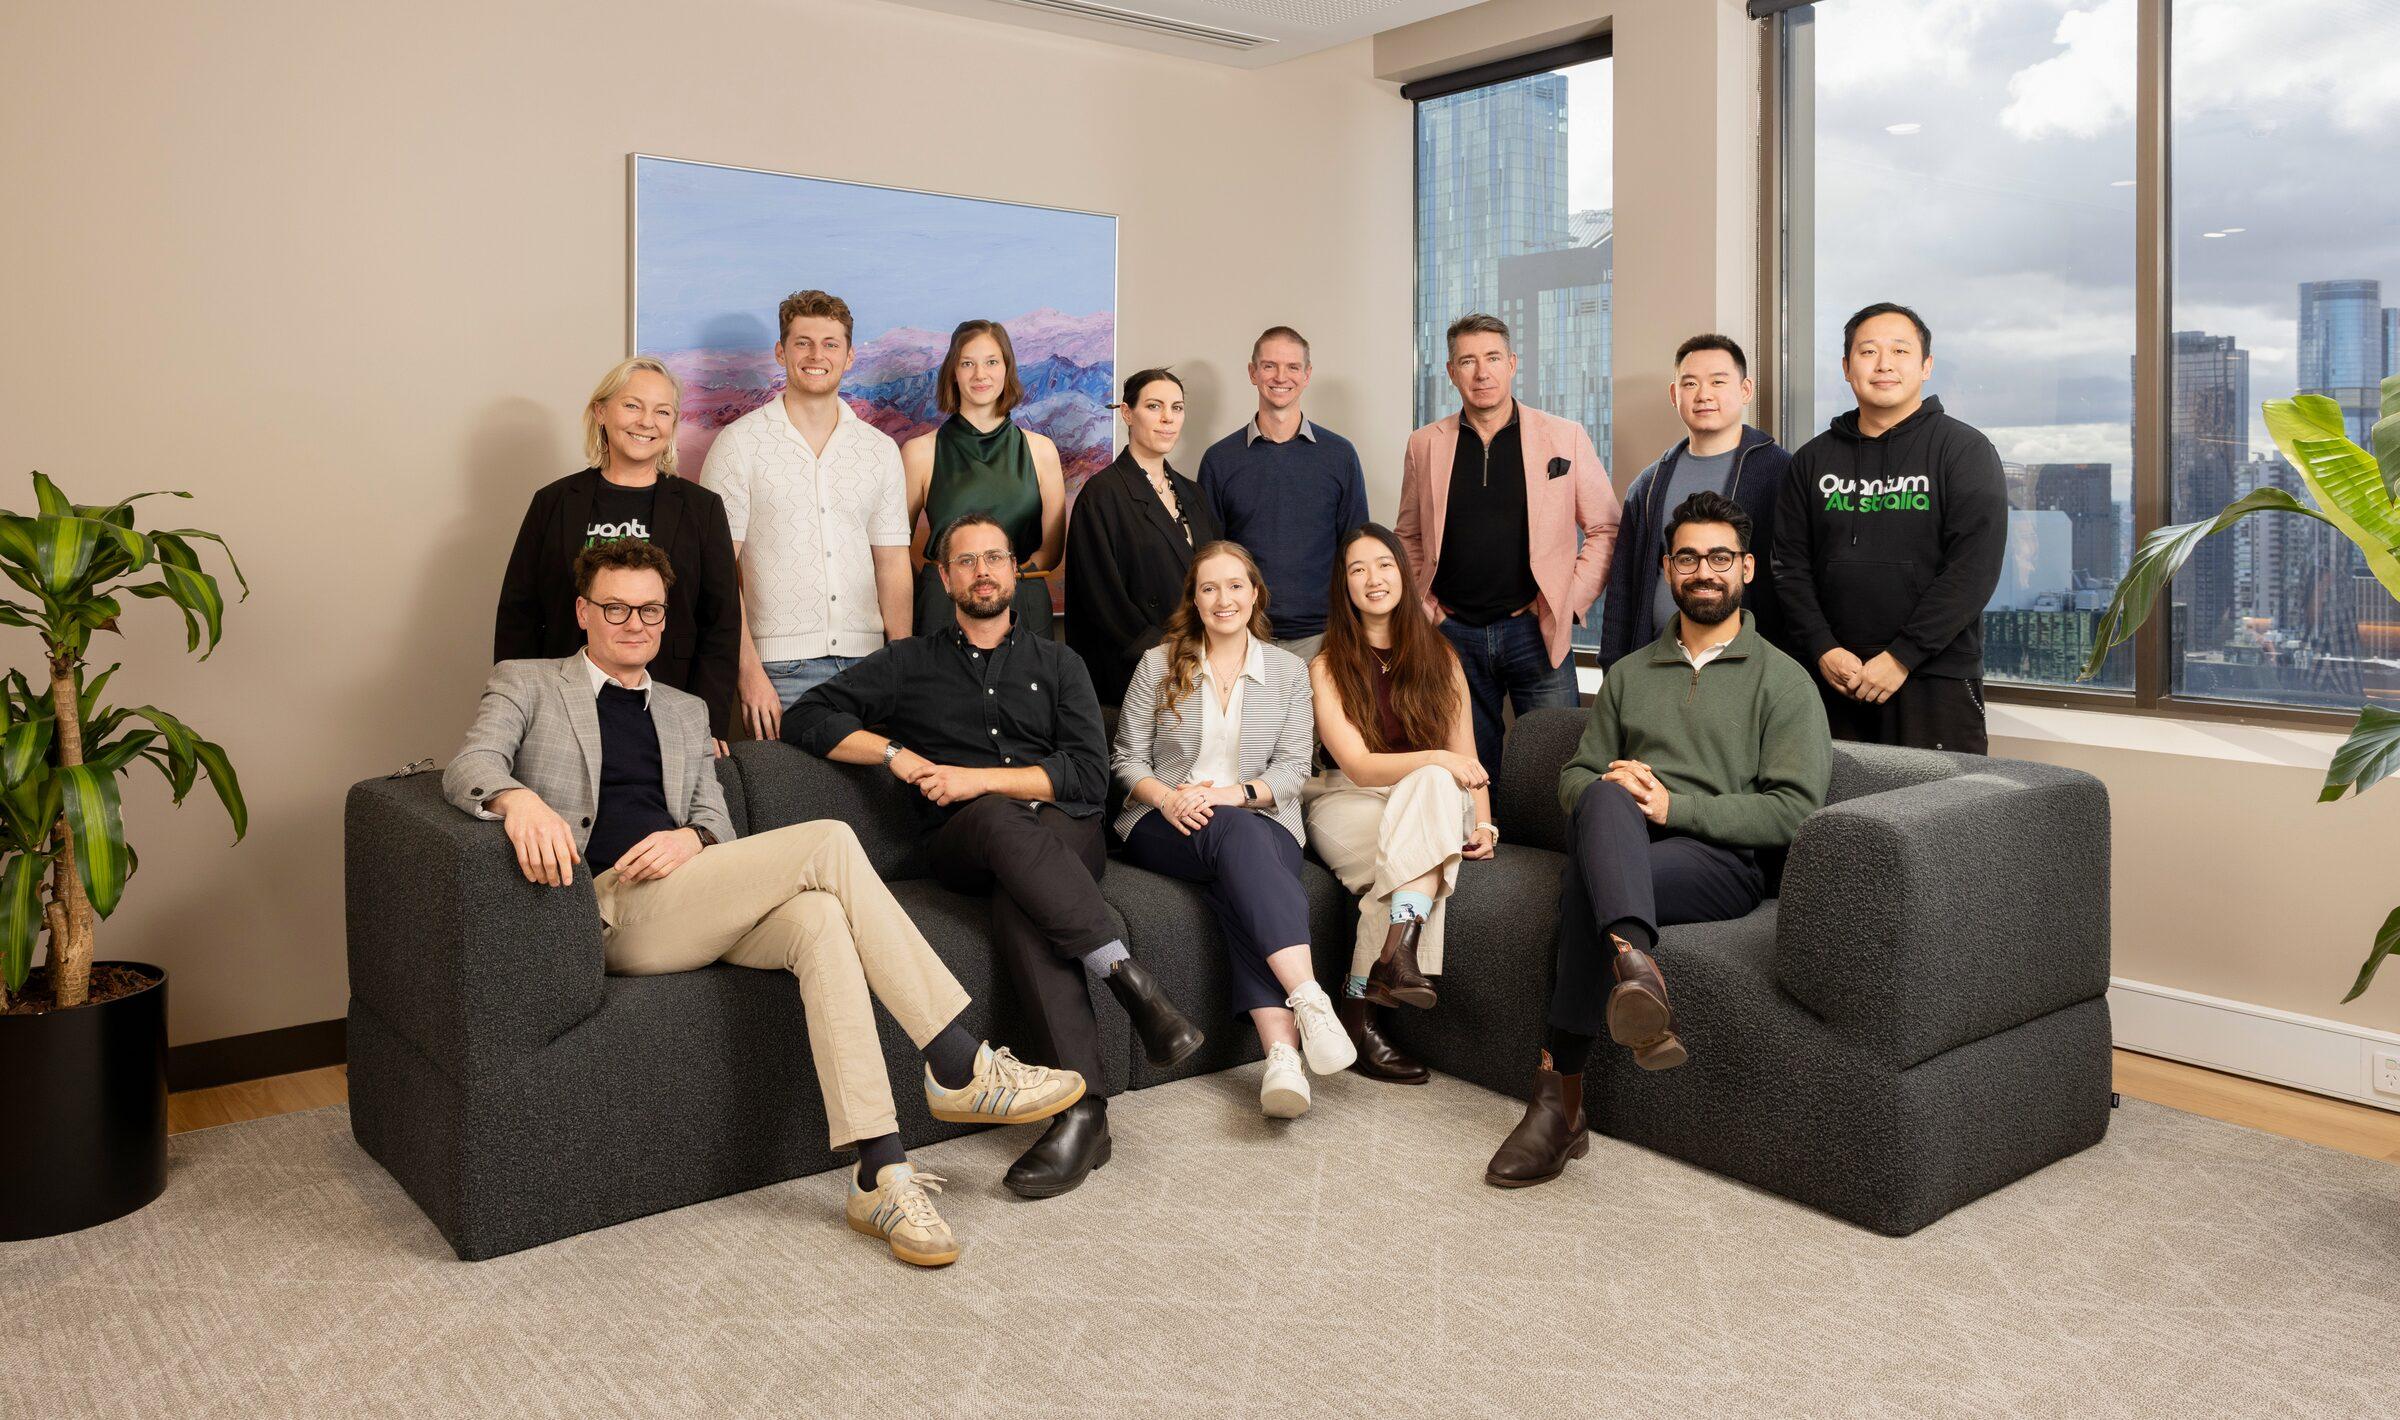
VeilNet selected for NextQ, Australia's national quantum accelerator
We're in the second cohort of NextQ, run by Quantum Australia and backed by the Australian Government. It's the next step in taking sovereign post-quantum networking from pre-release to market.
The third generation of VeilNet: post-quantum from the root up
We started building on NIST's new post-quantum standards in February 2025. The third generation is here: a post-quantum PKI tree for identity, a gossip mesh keyed with ML-KEM, AI-driven routing and a high-performance Go core, open for evaluation now.