Manage every identity and certificate.
Control who can sign in and what each role can do, see who owns every node and certificate, and issue, renew and revoke post-quantum certificates from your own certificate authorities, all on infrastructure you own.
Every identity and certificate in one place.
Sign in with the guardian's built-in identity service or your existing identity provider. Every certificate is issued by an authority whose private key never leaves the guardian.
/ 05
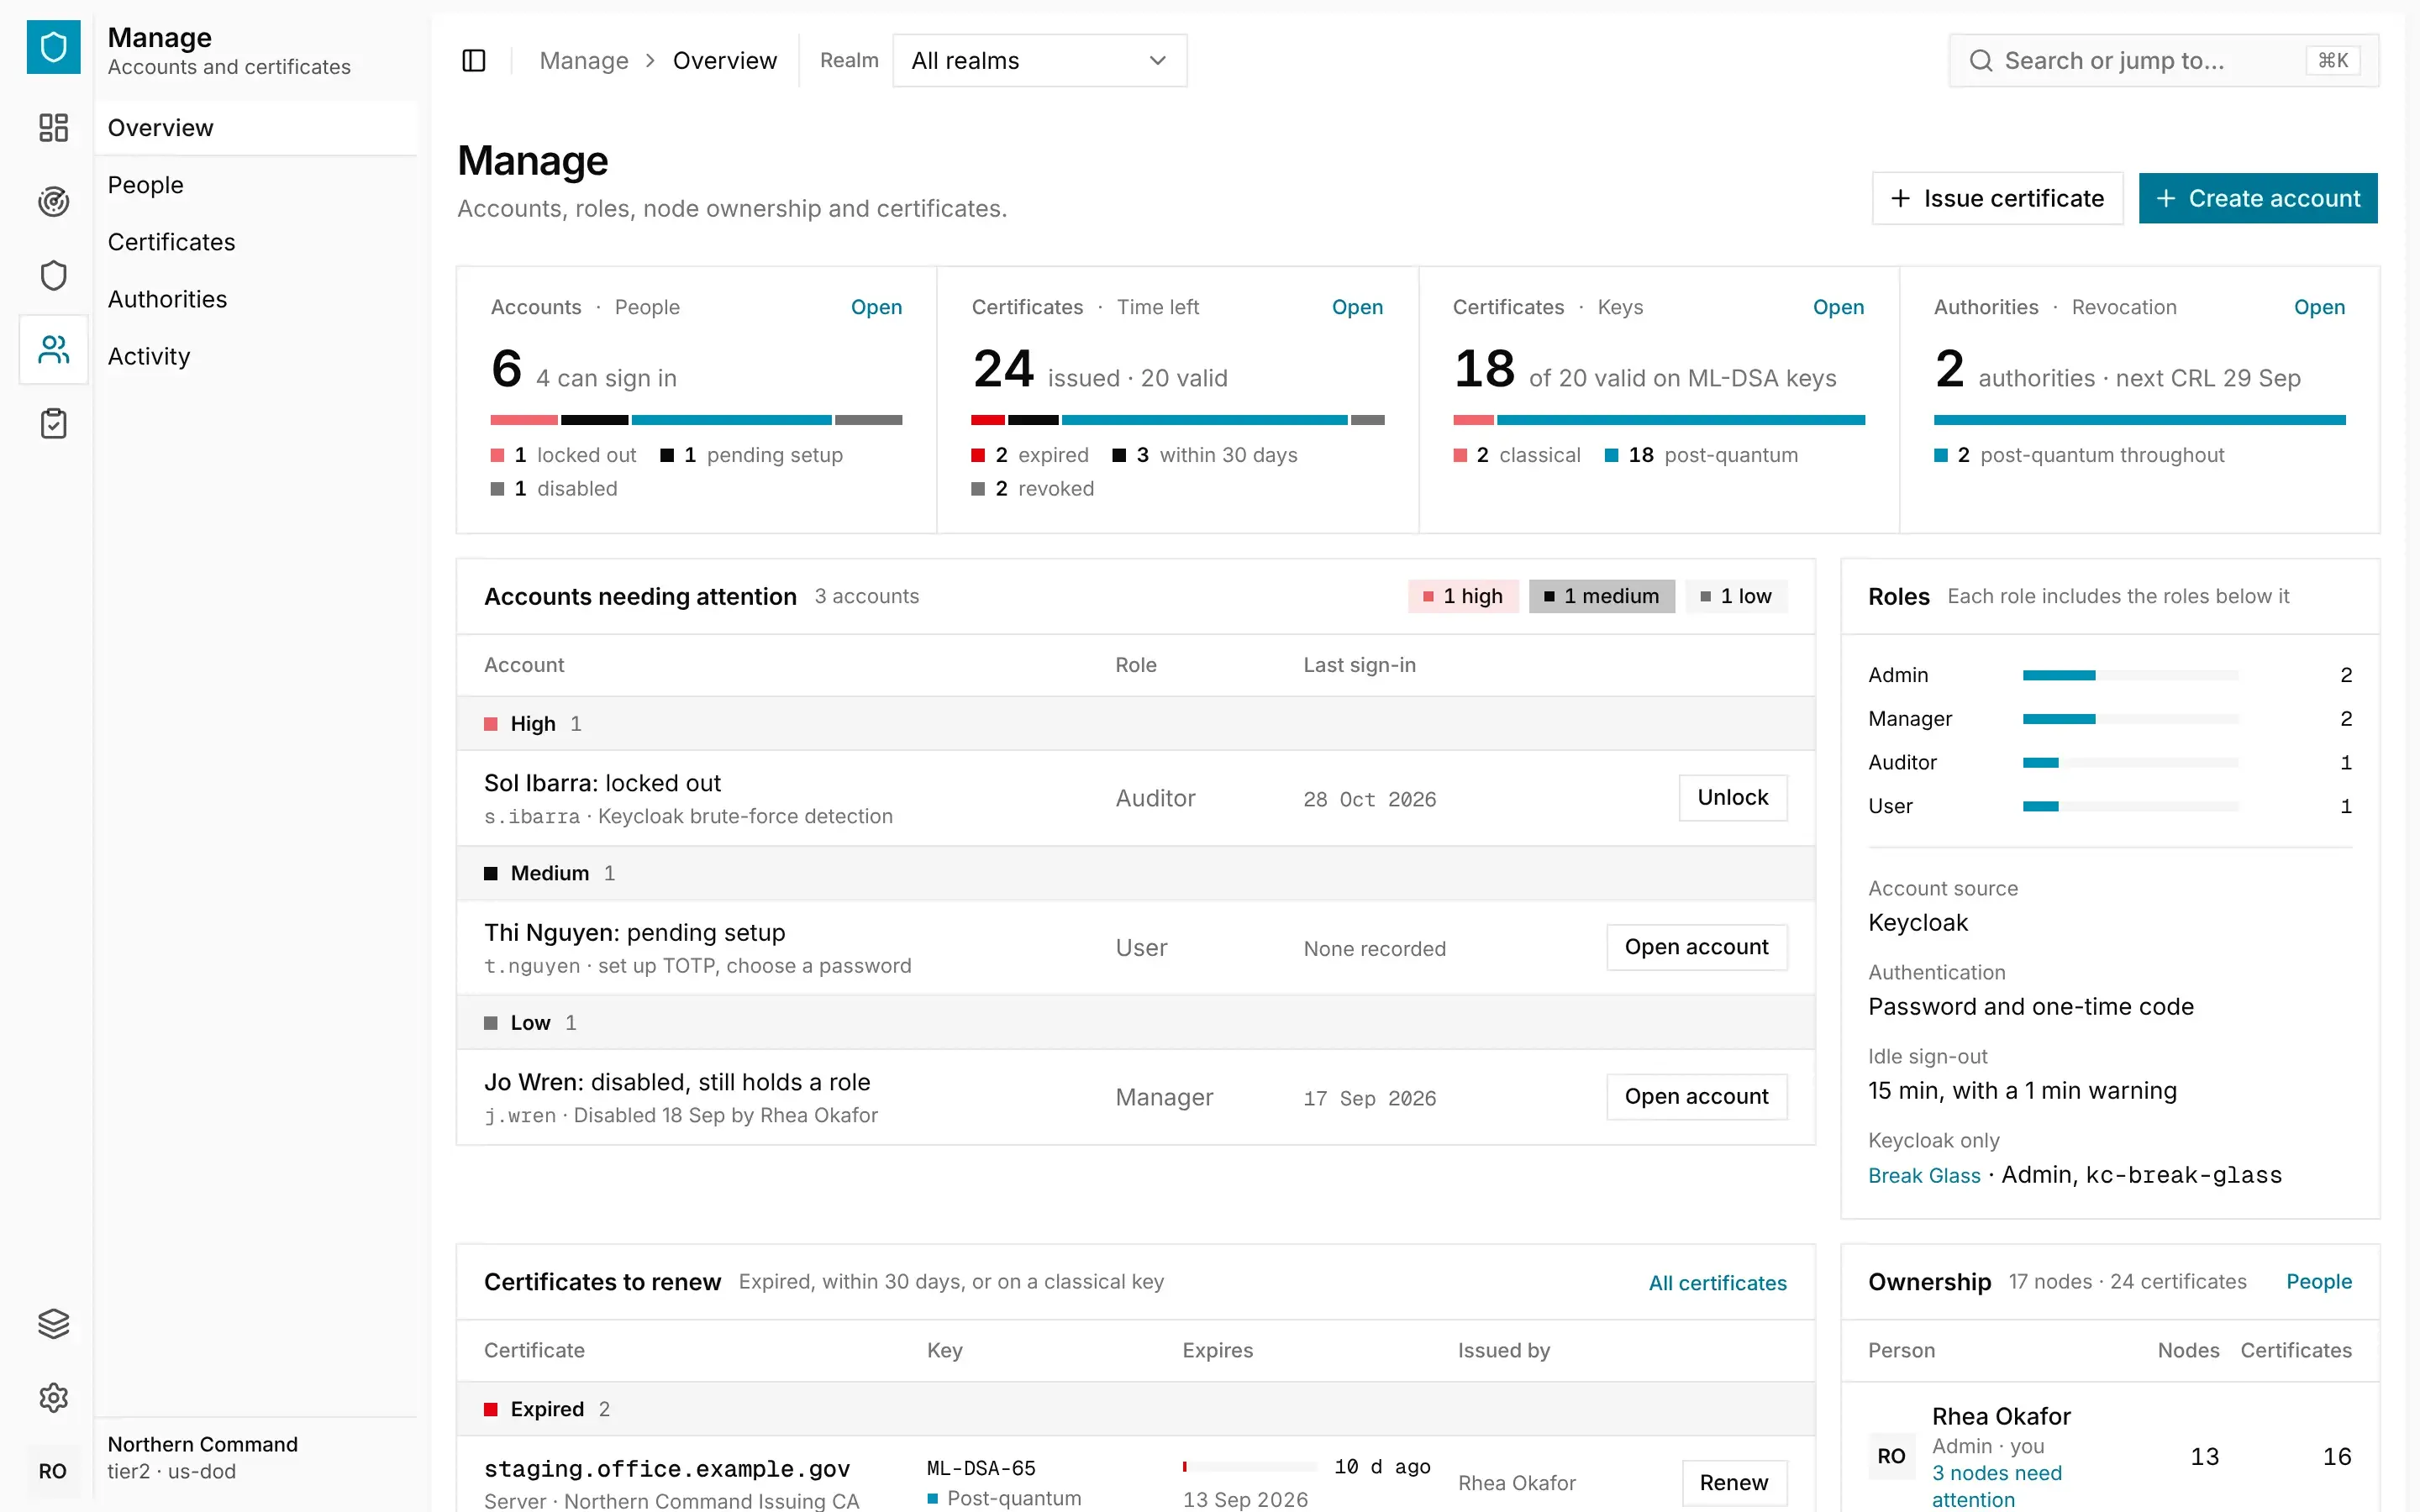
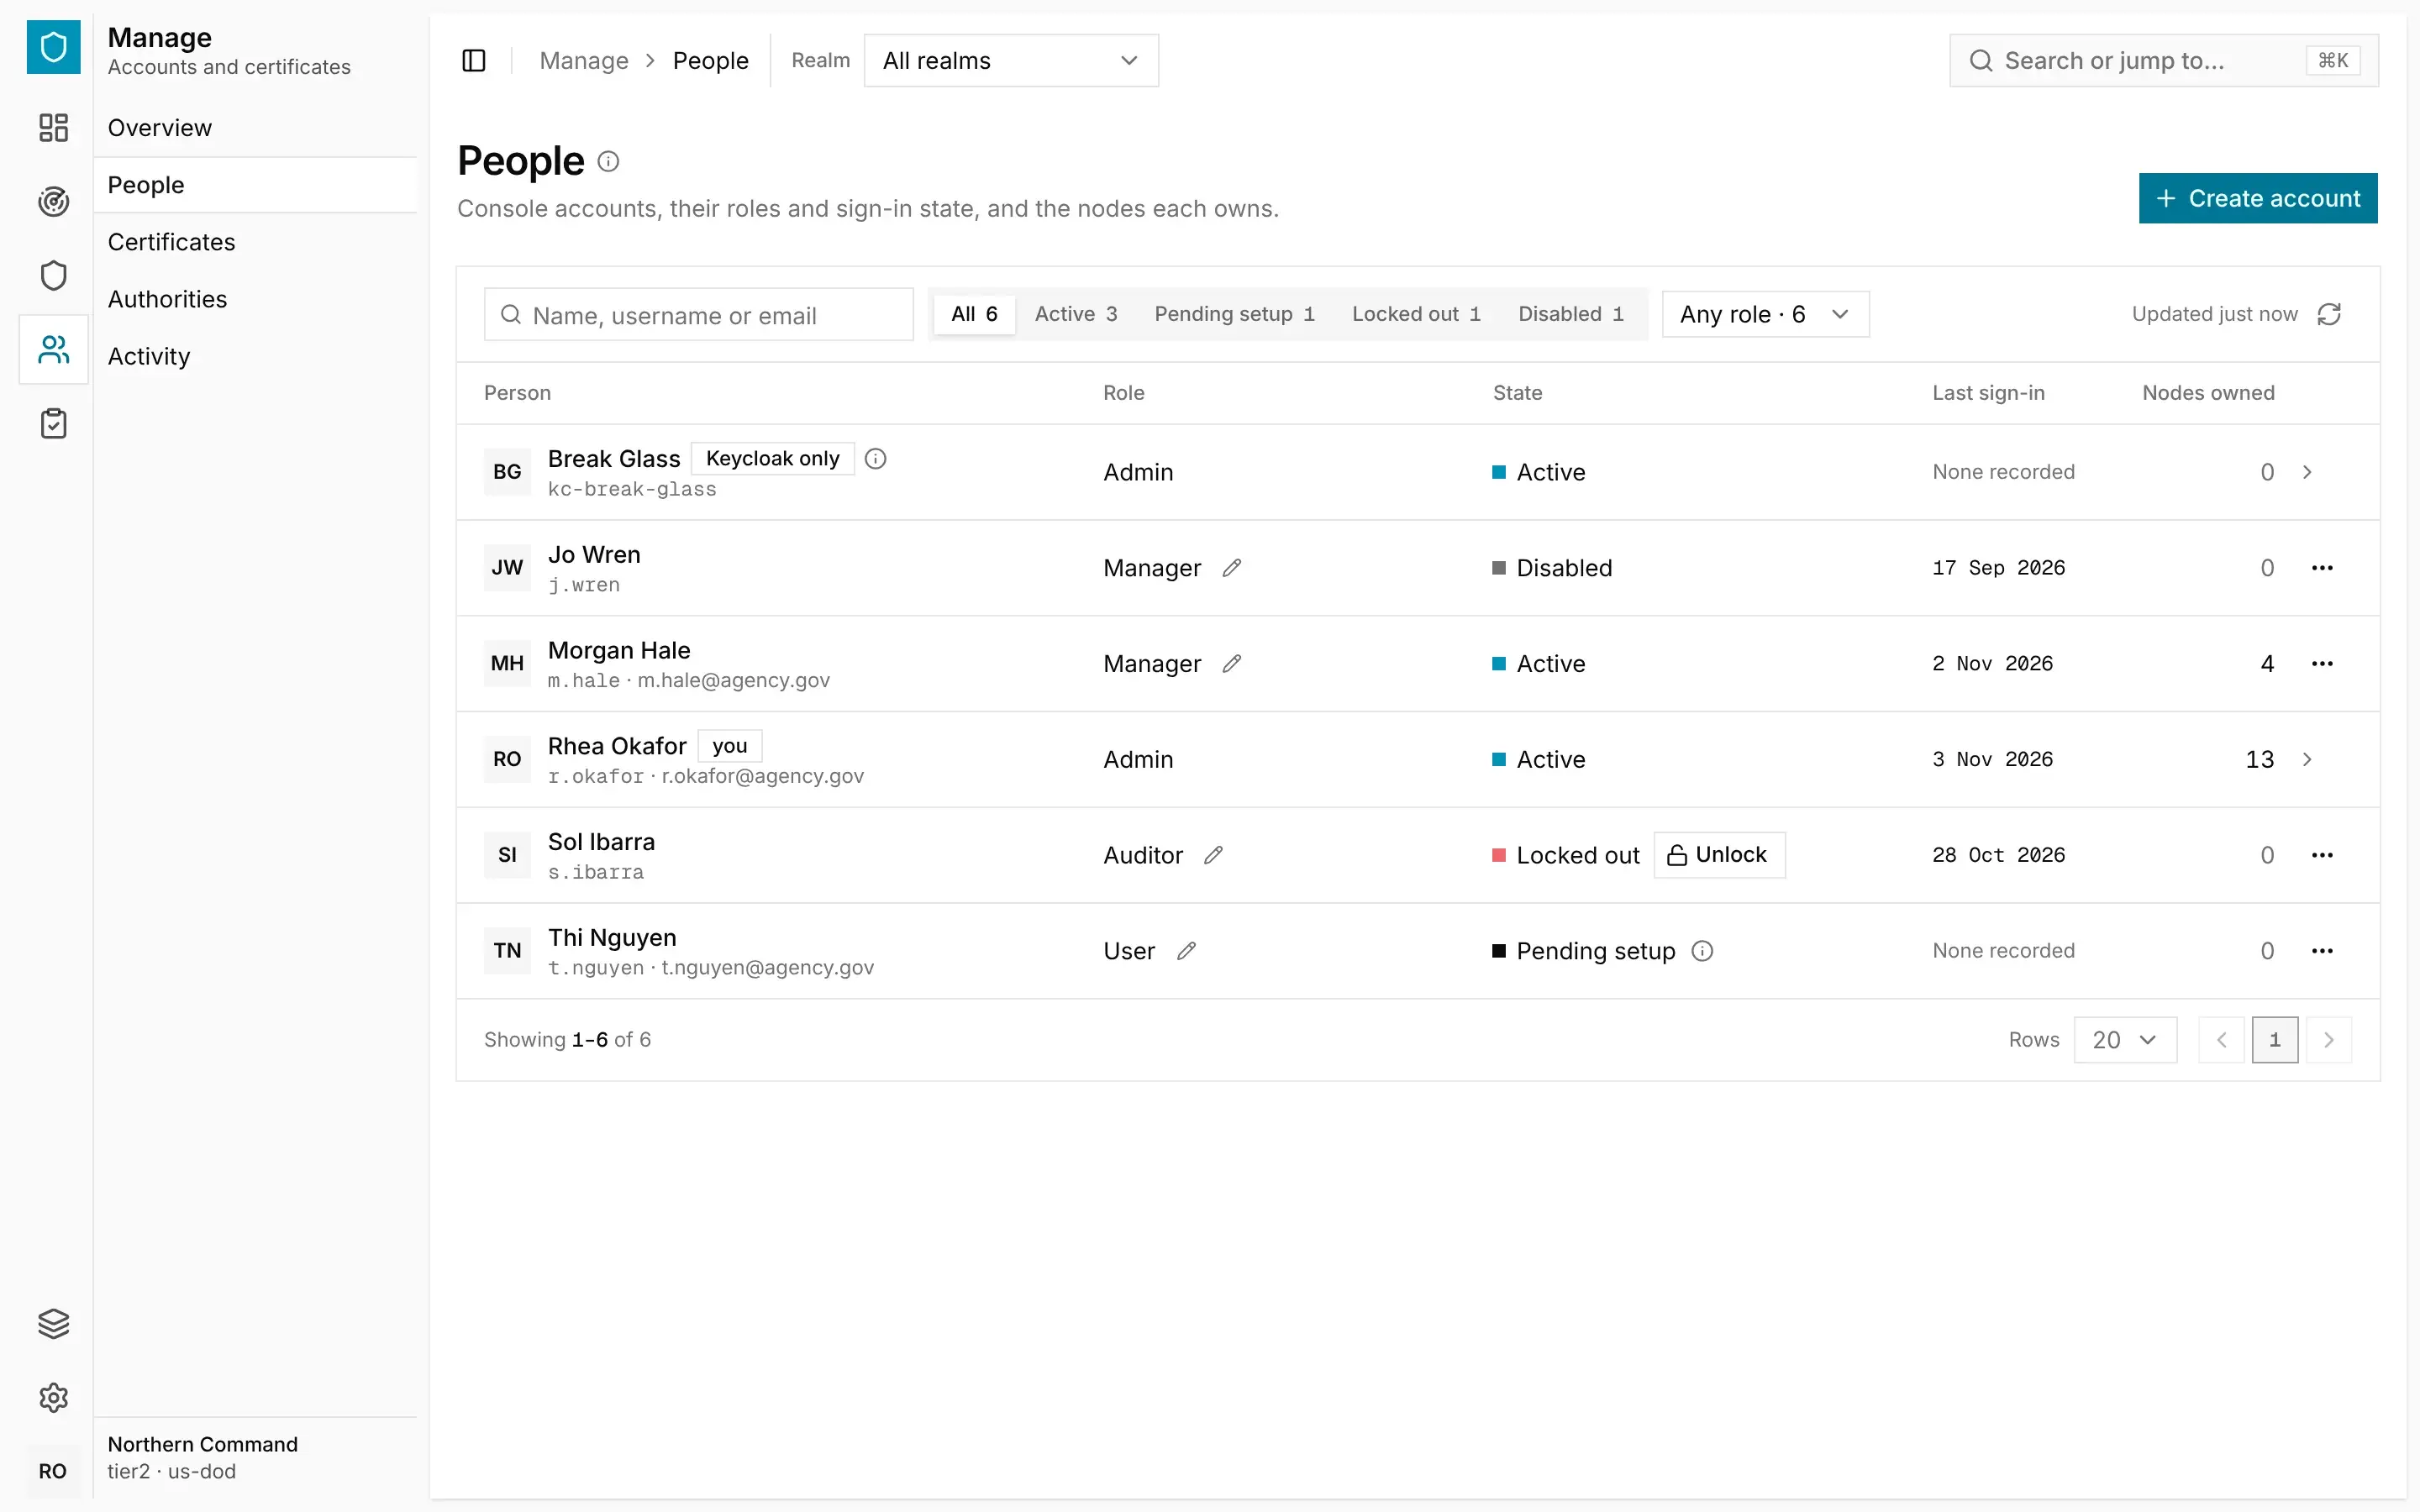
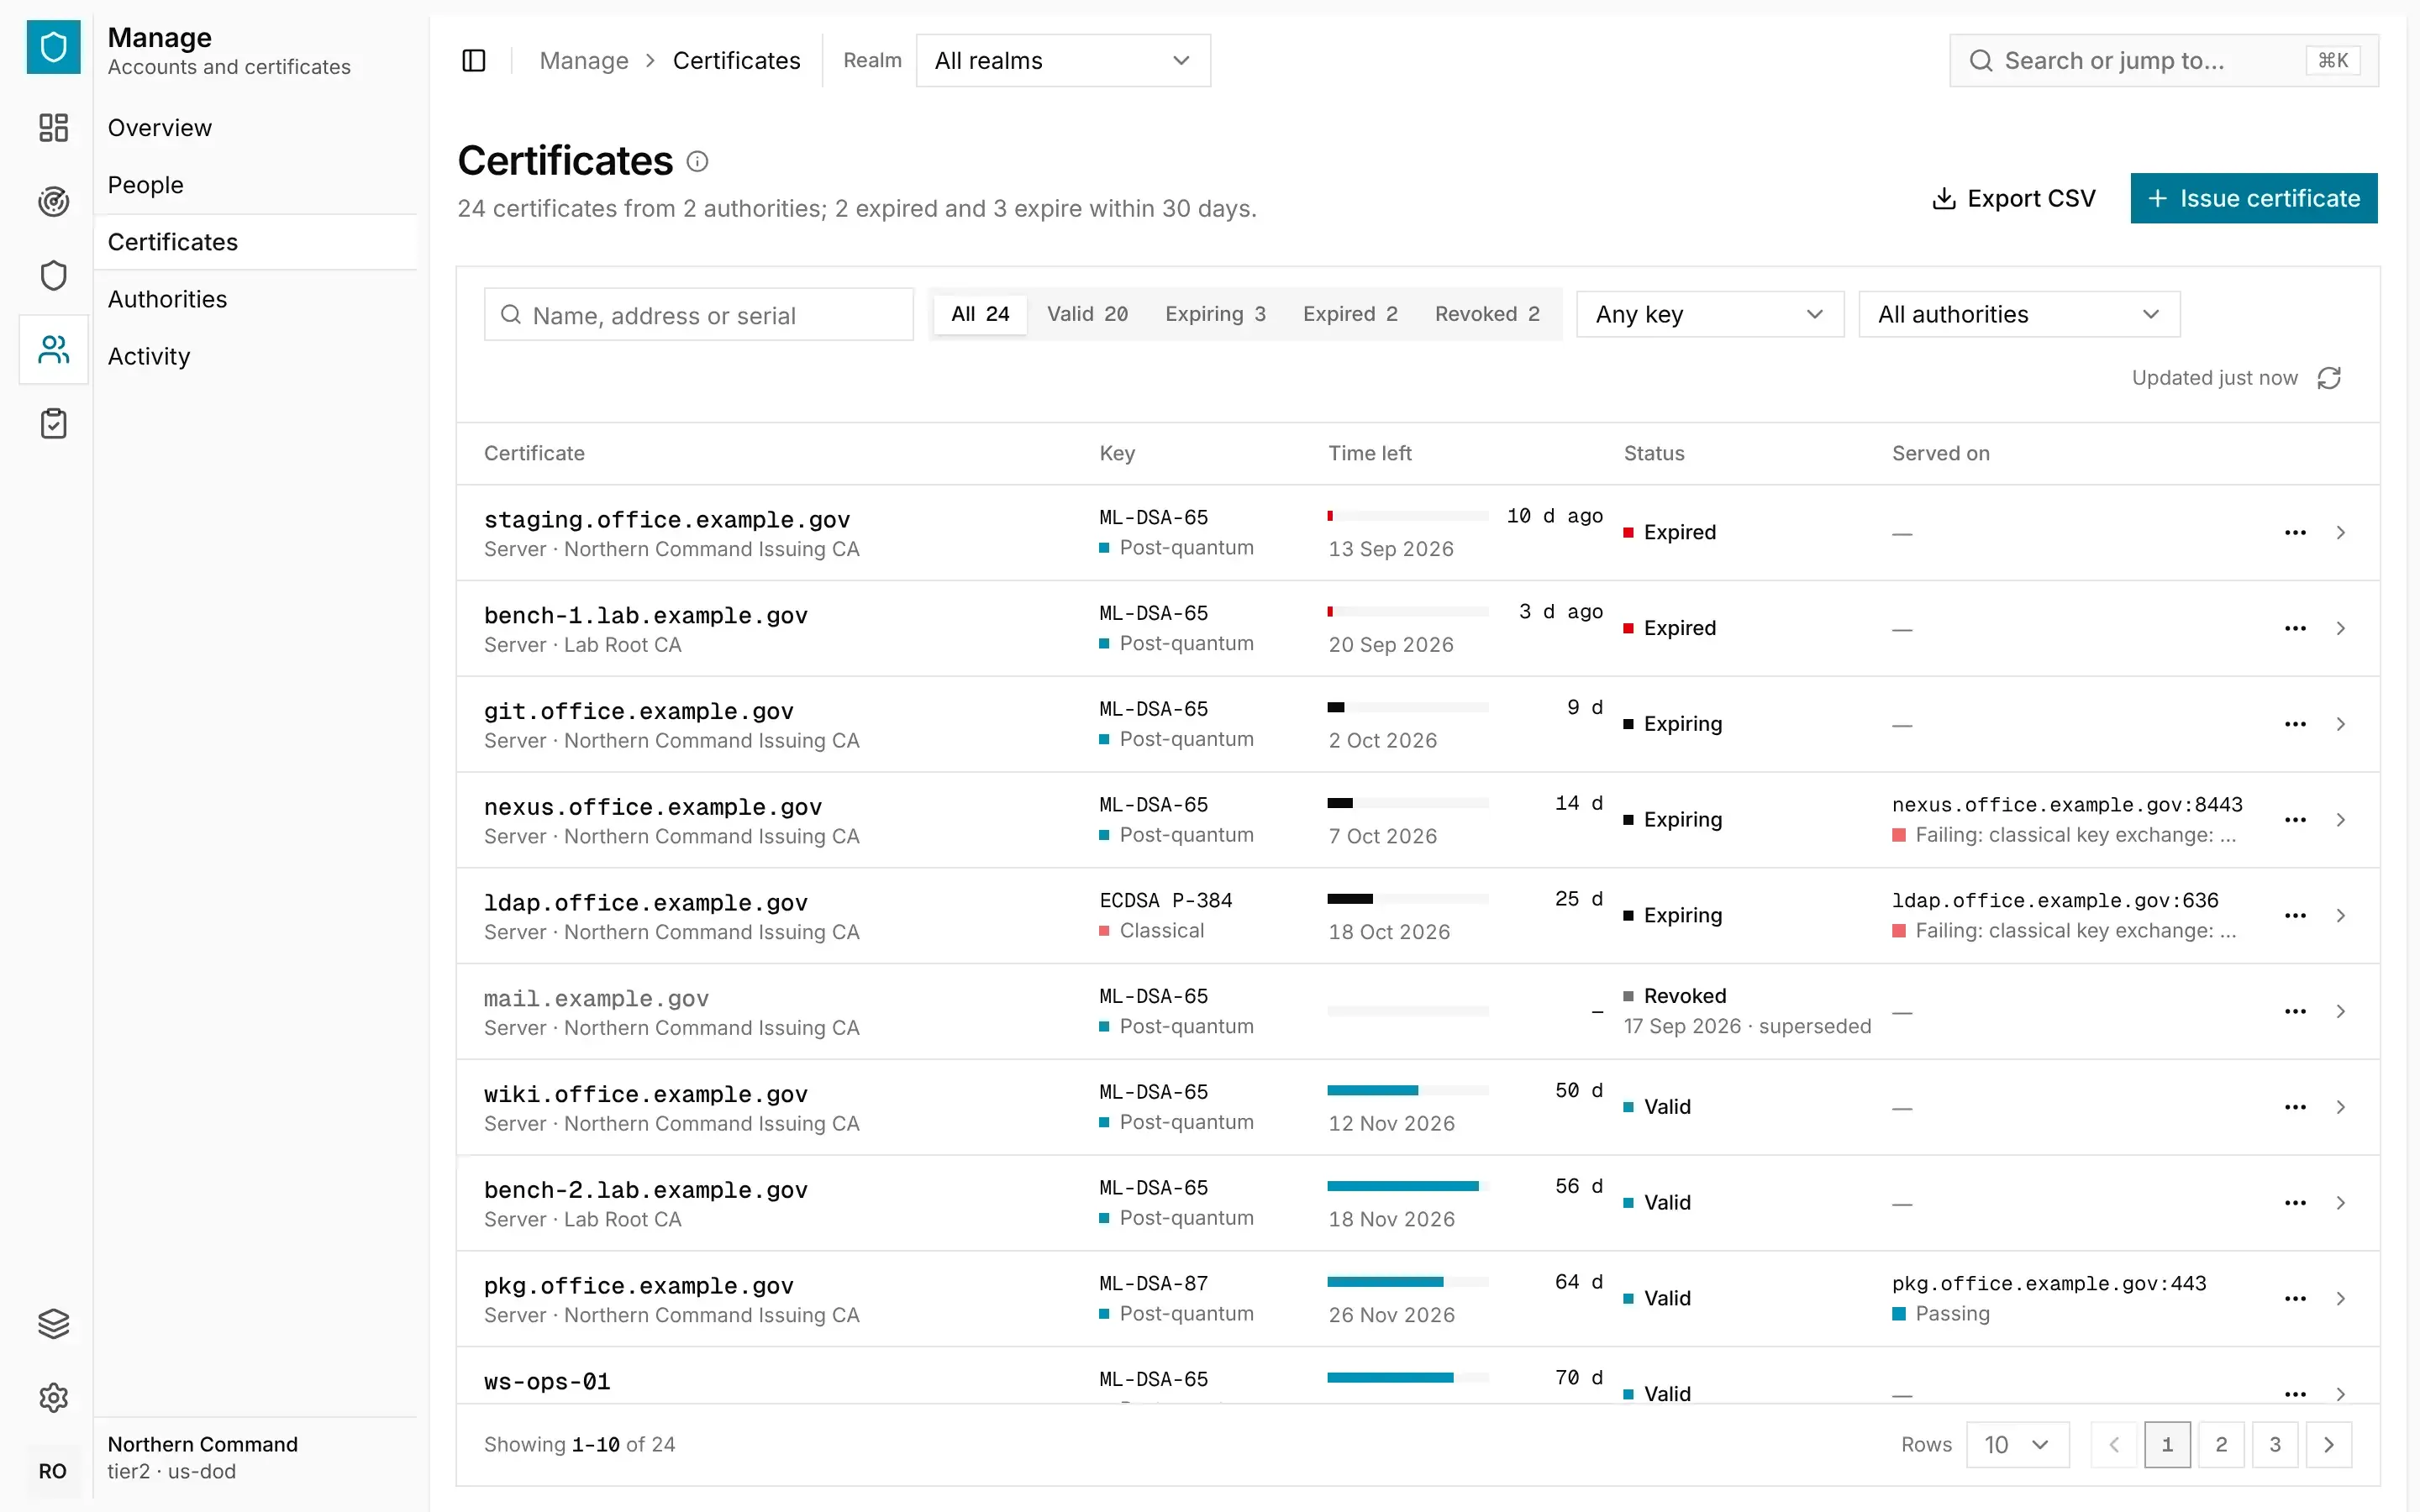
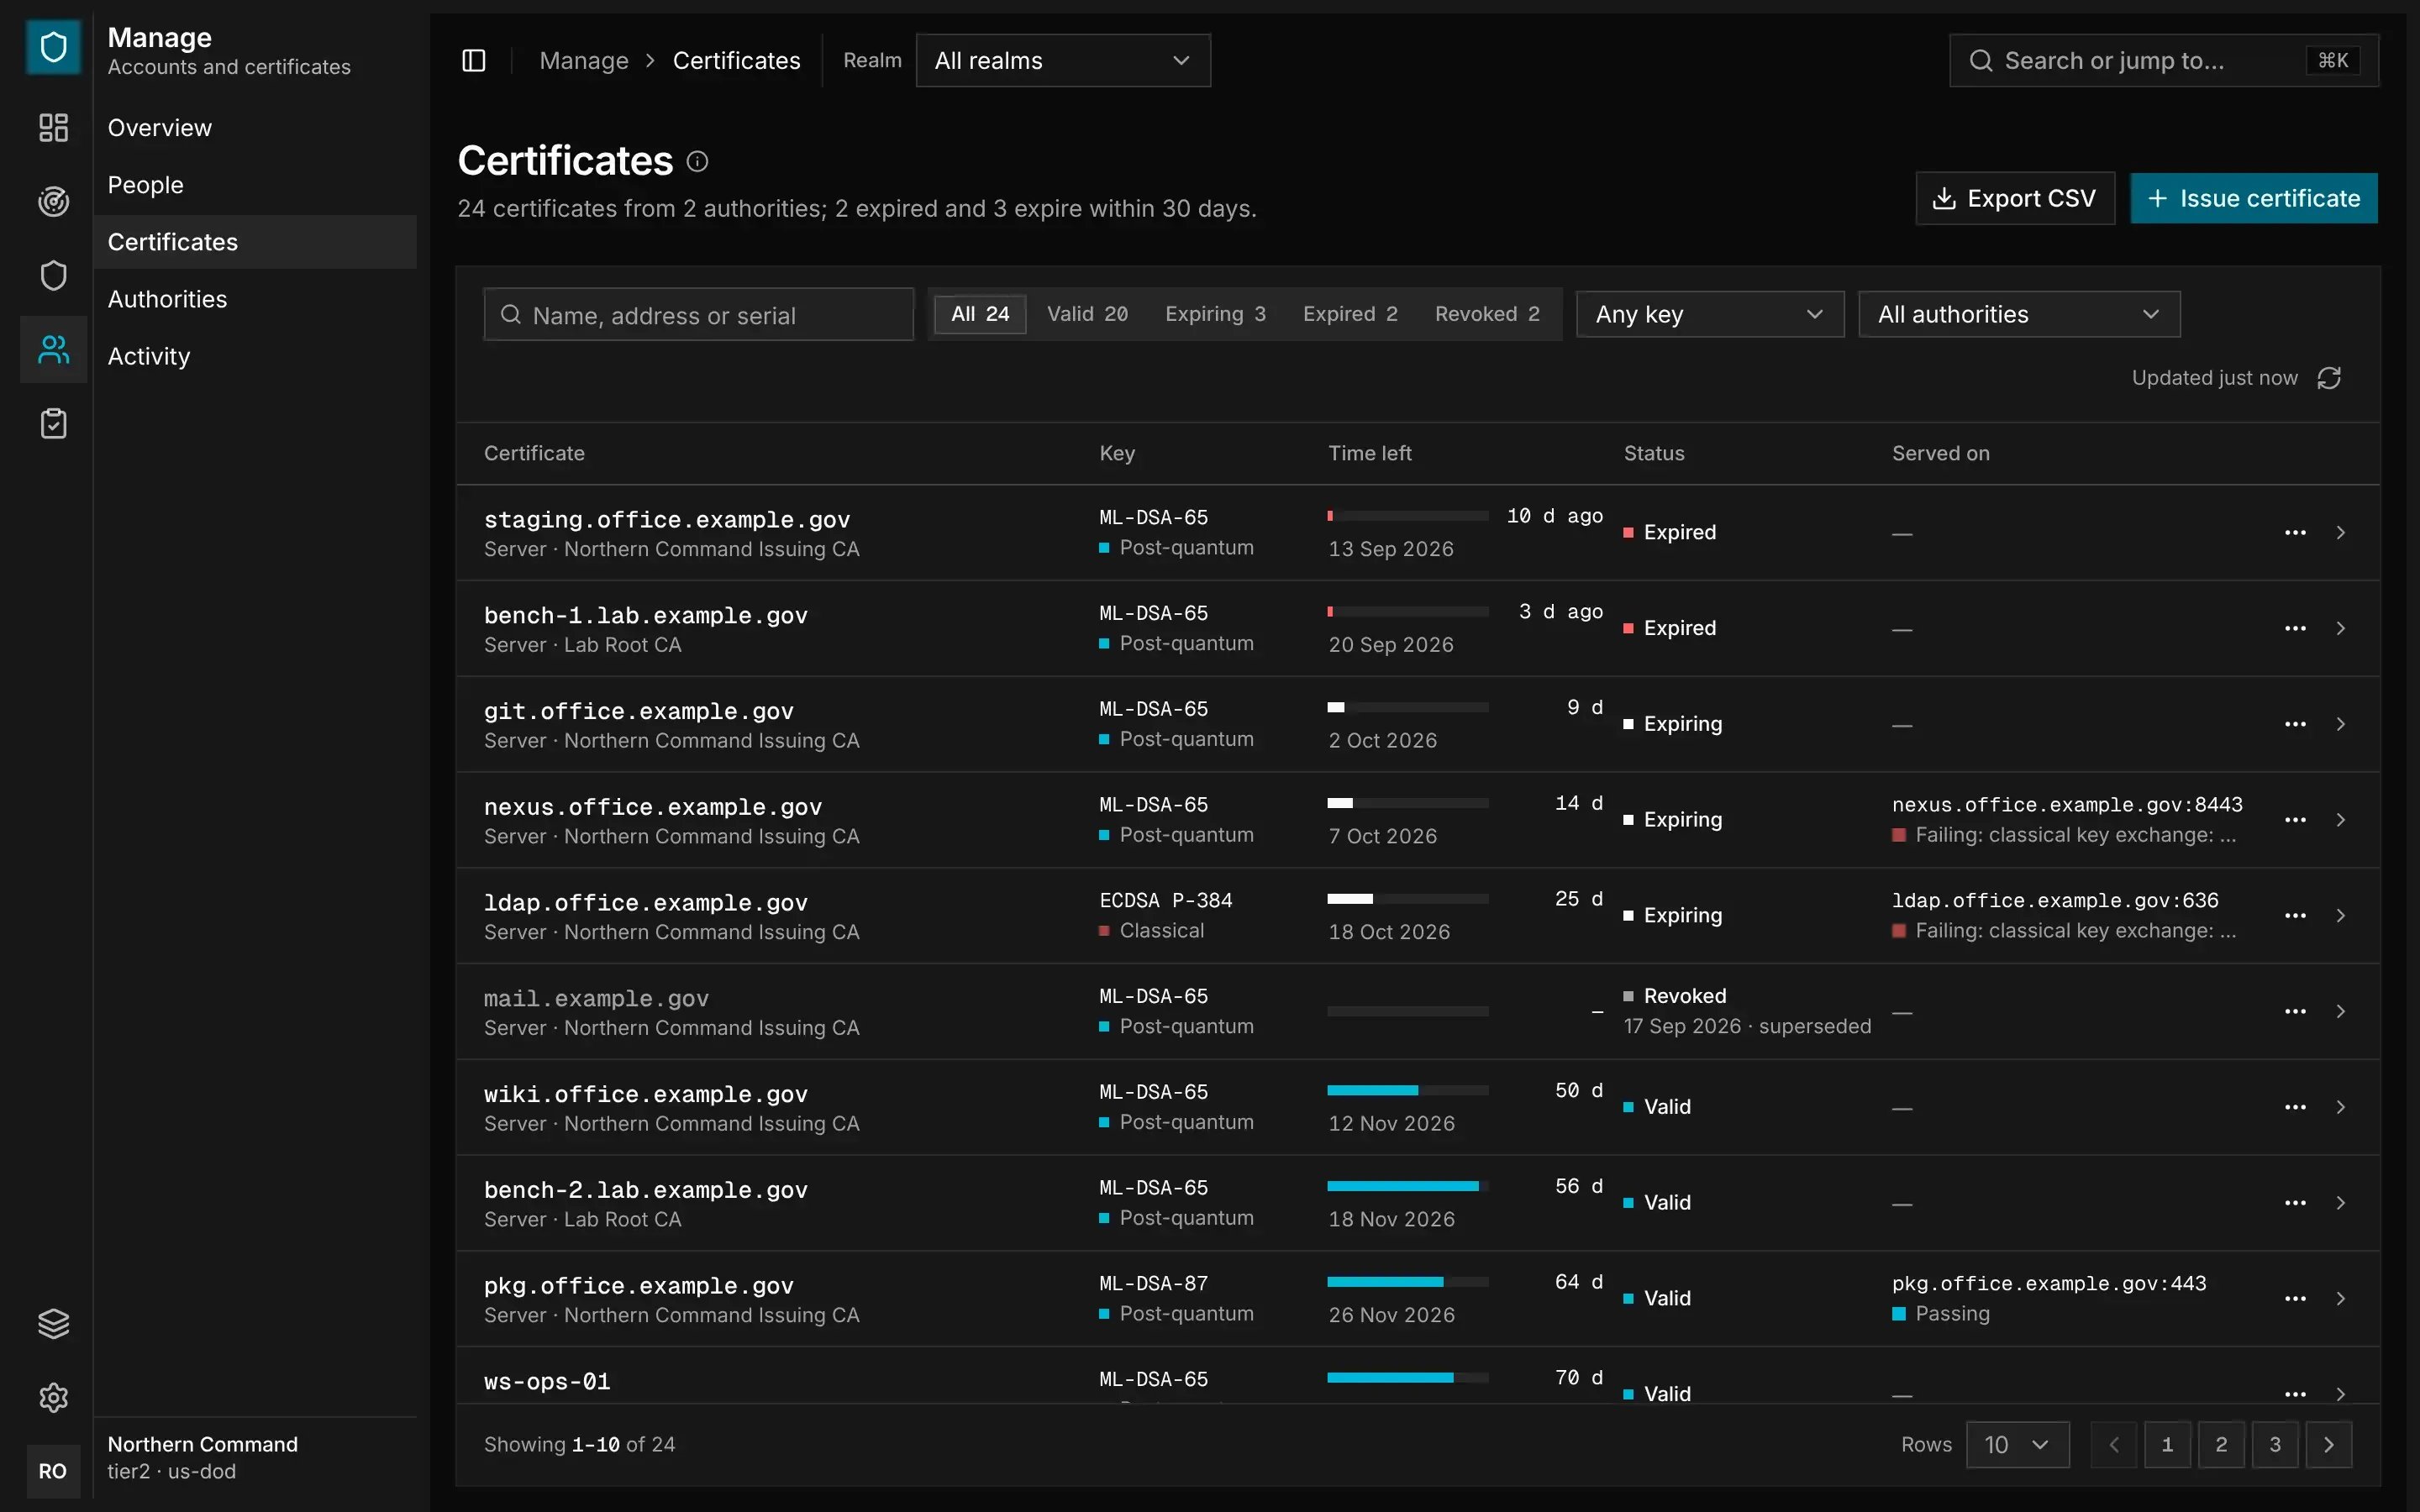
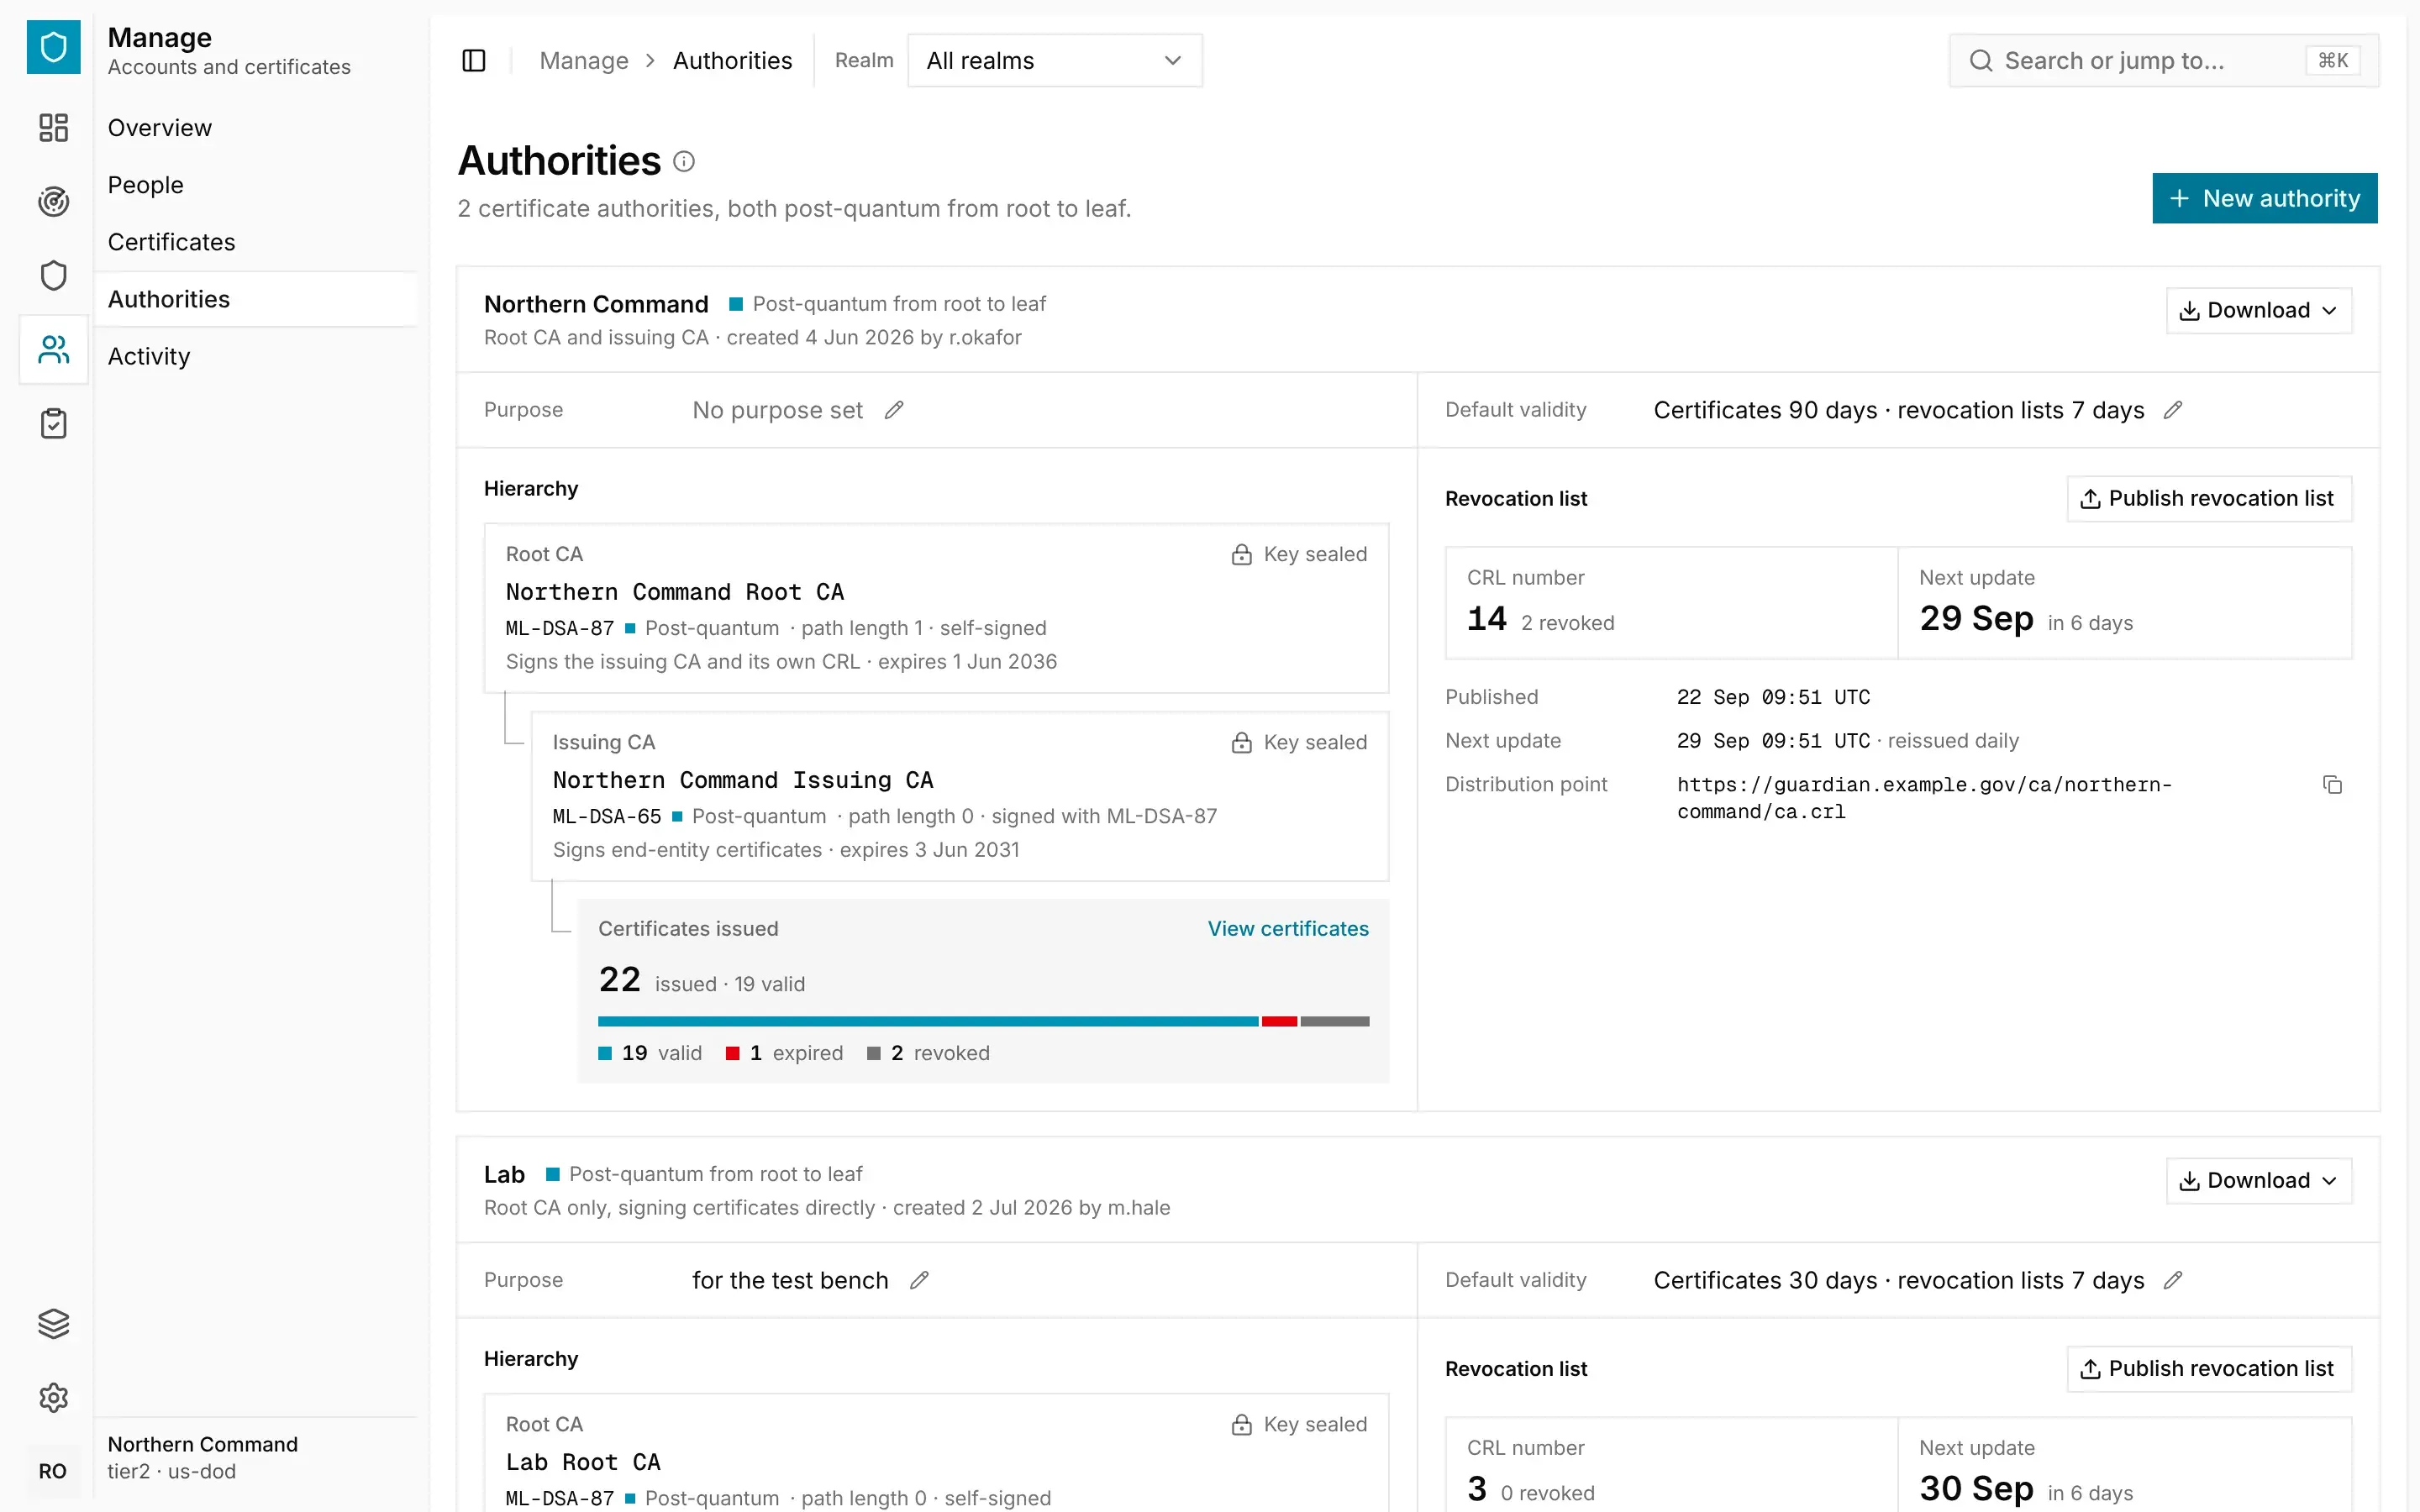
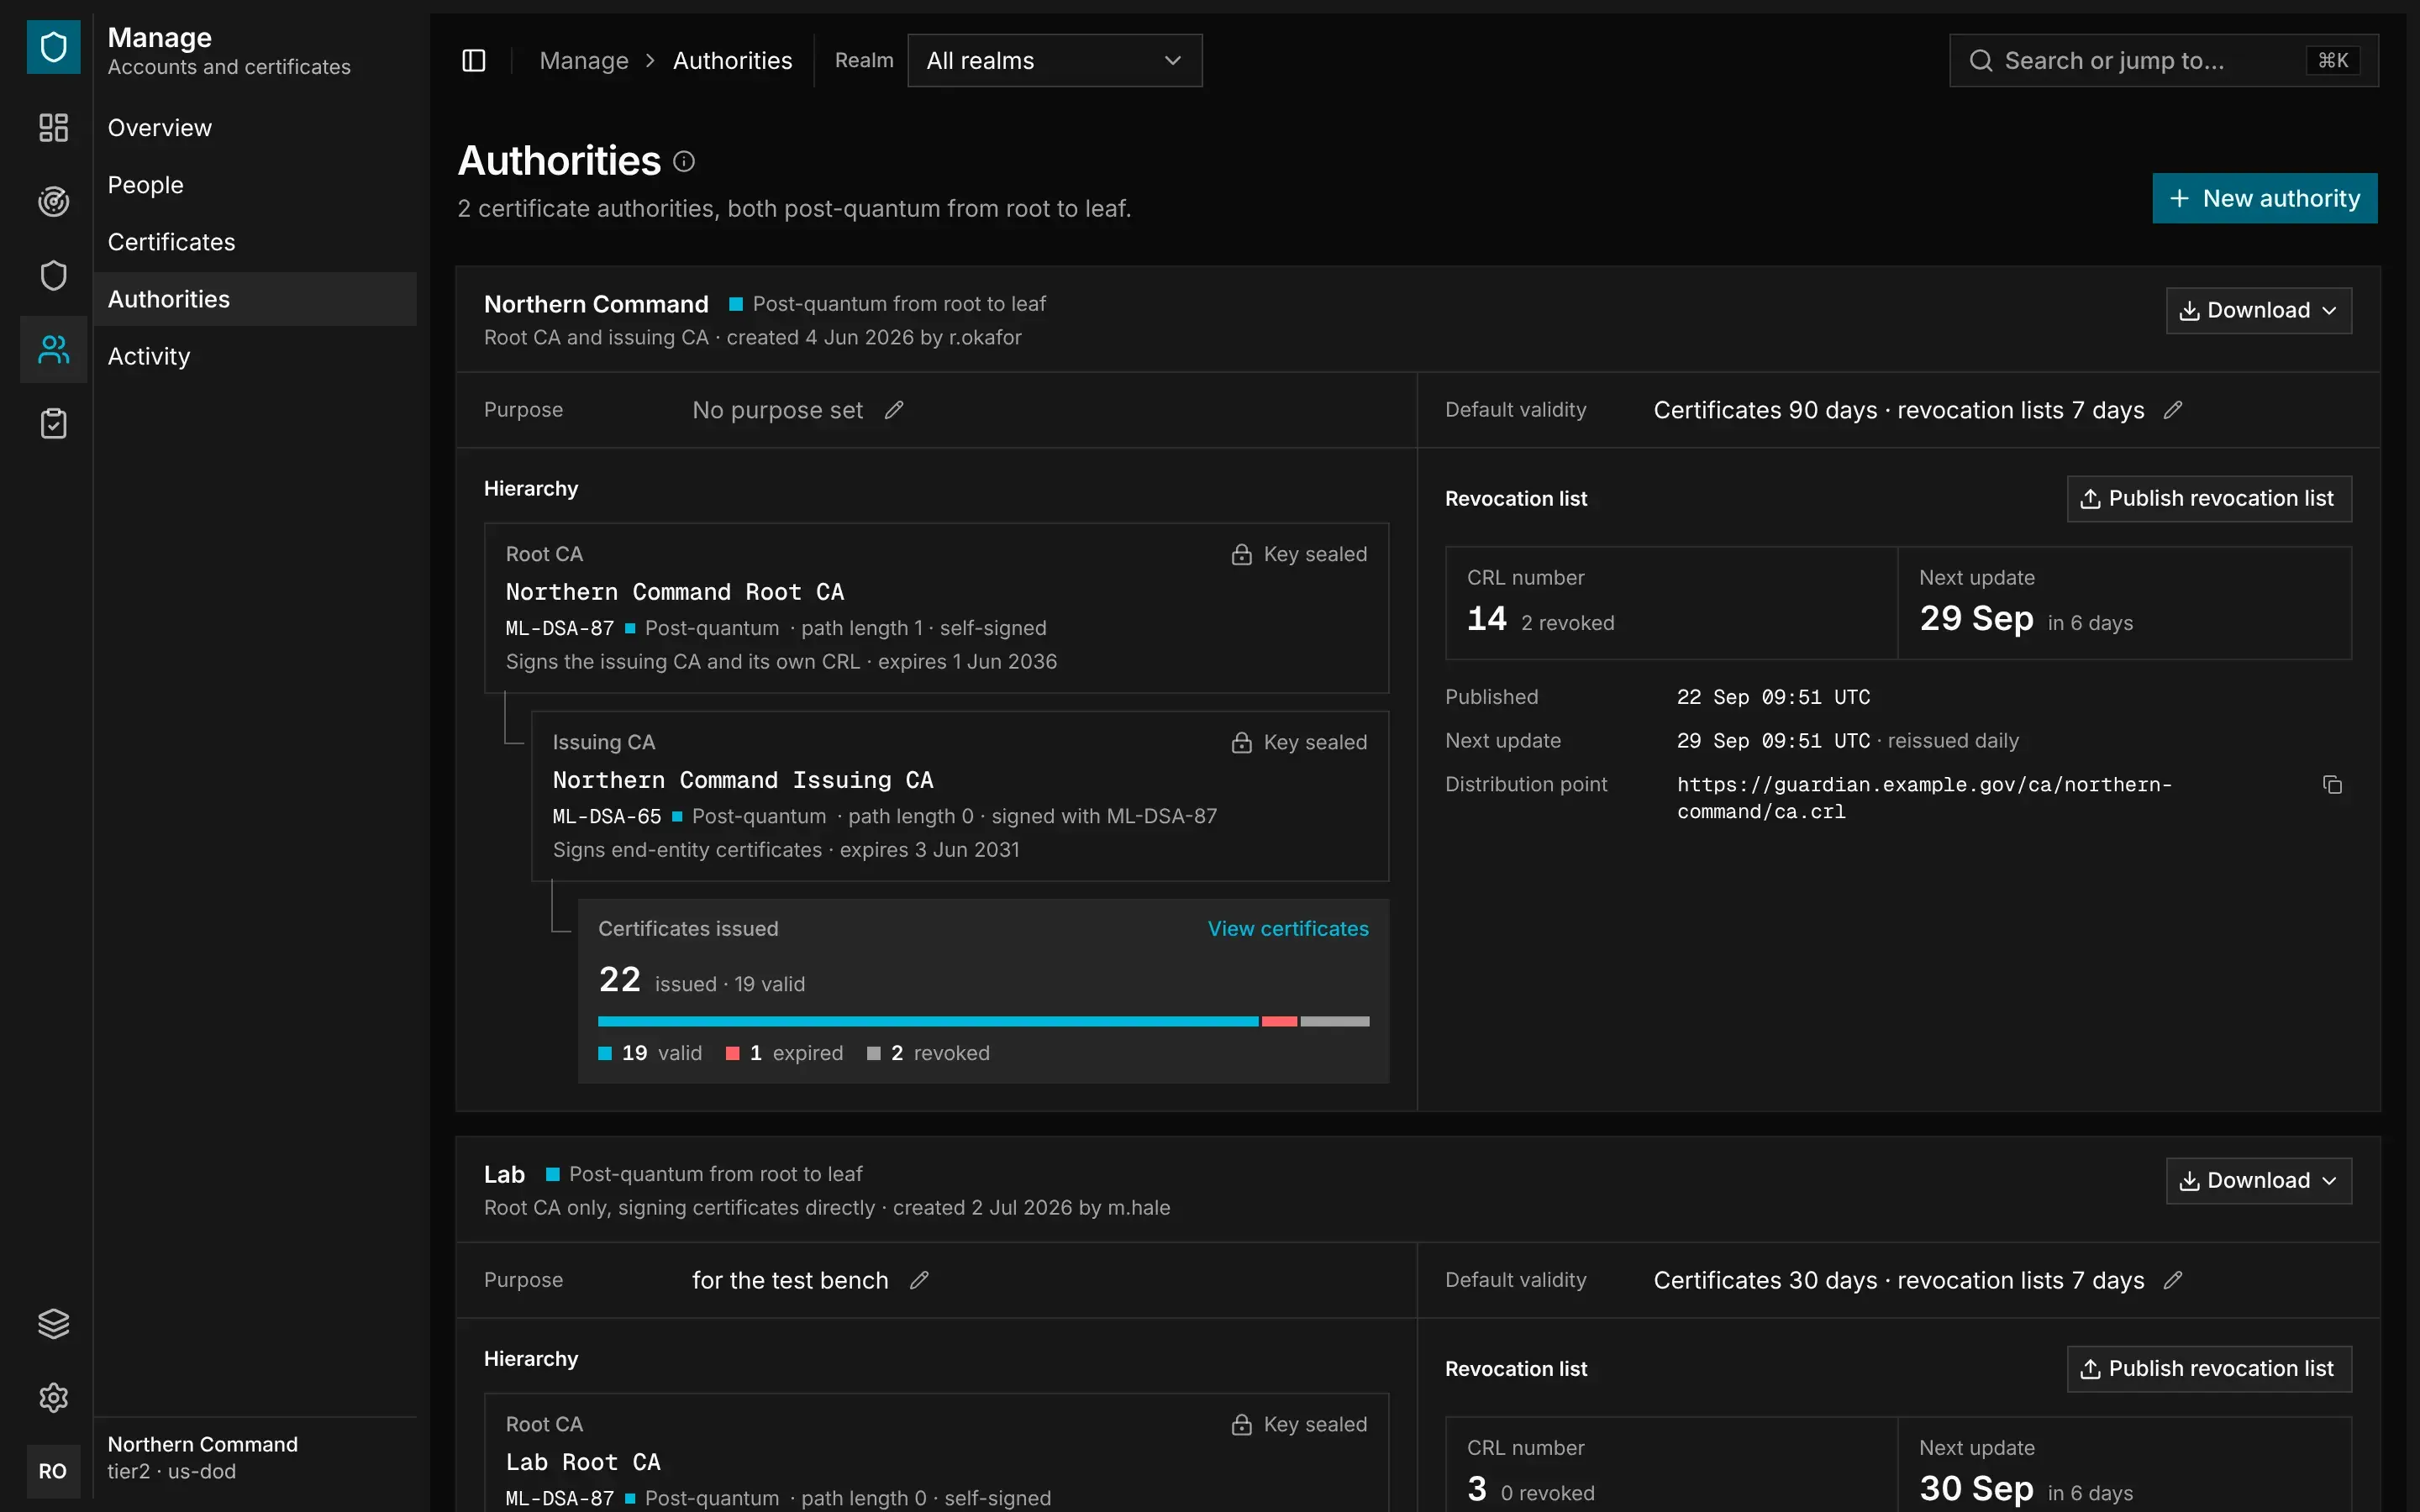
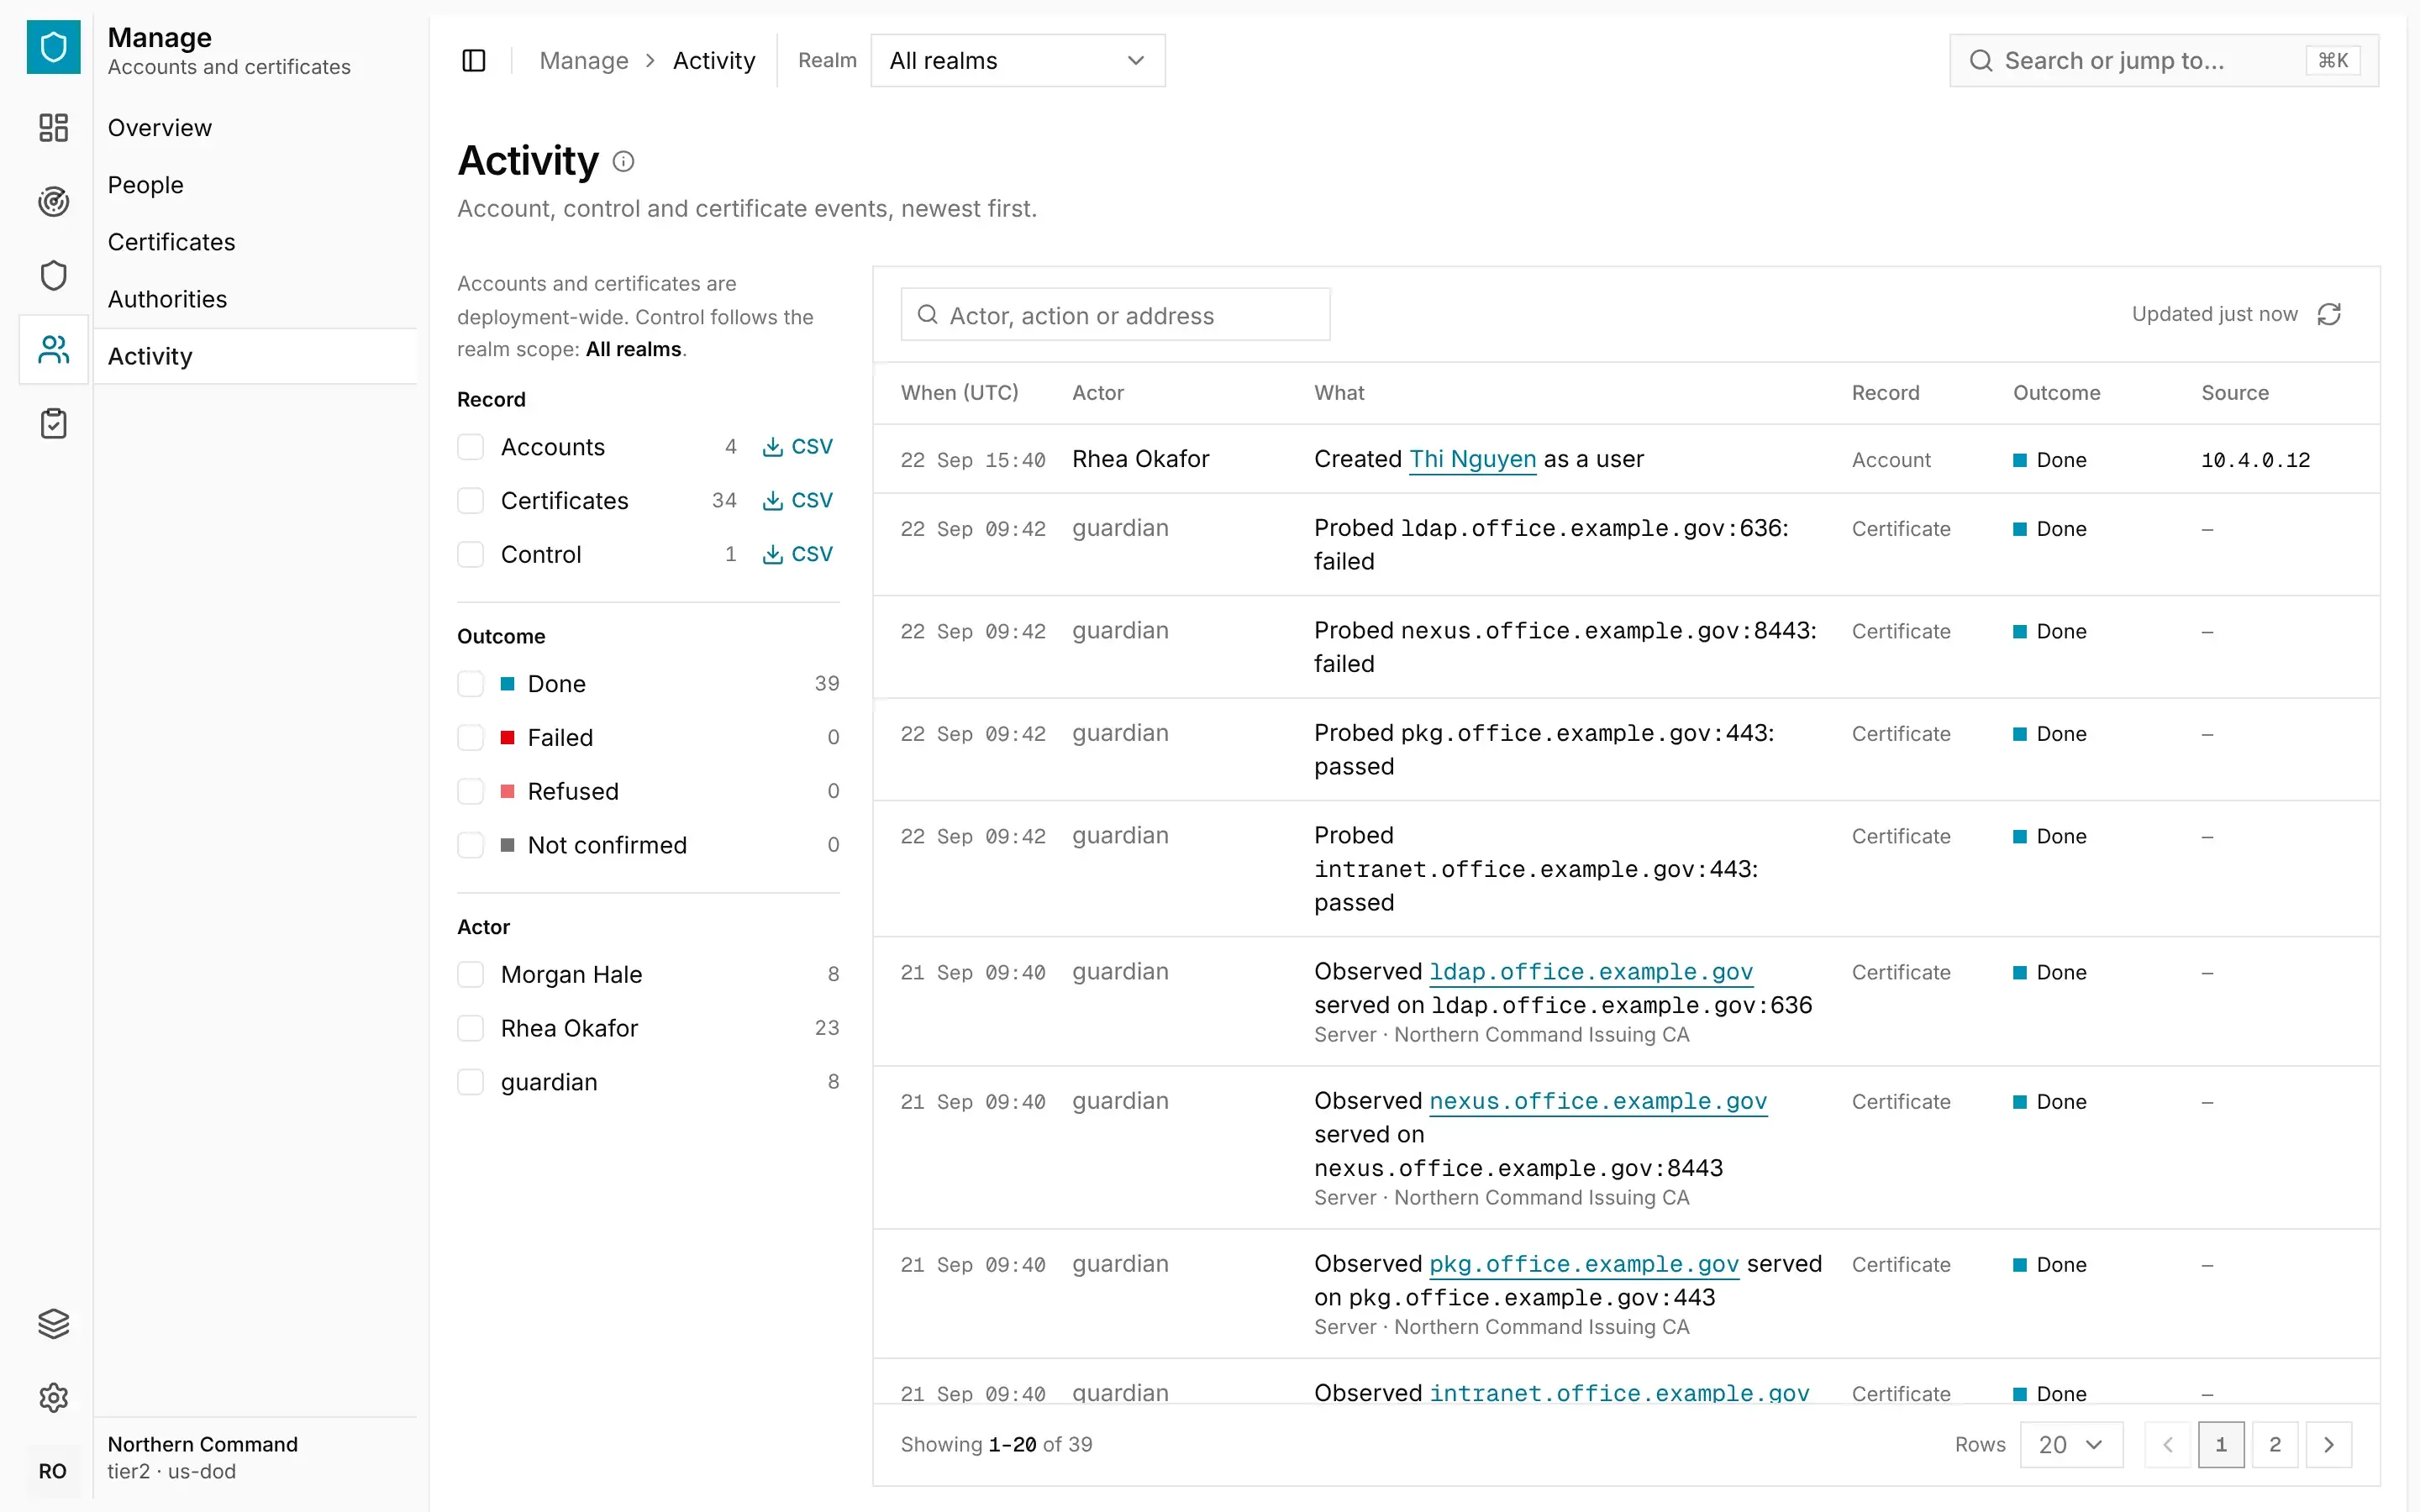
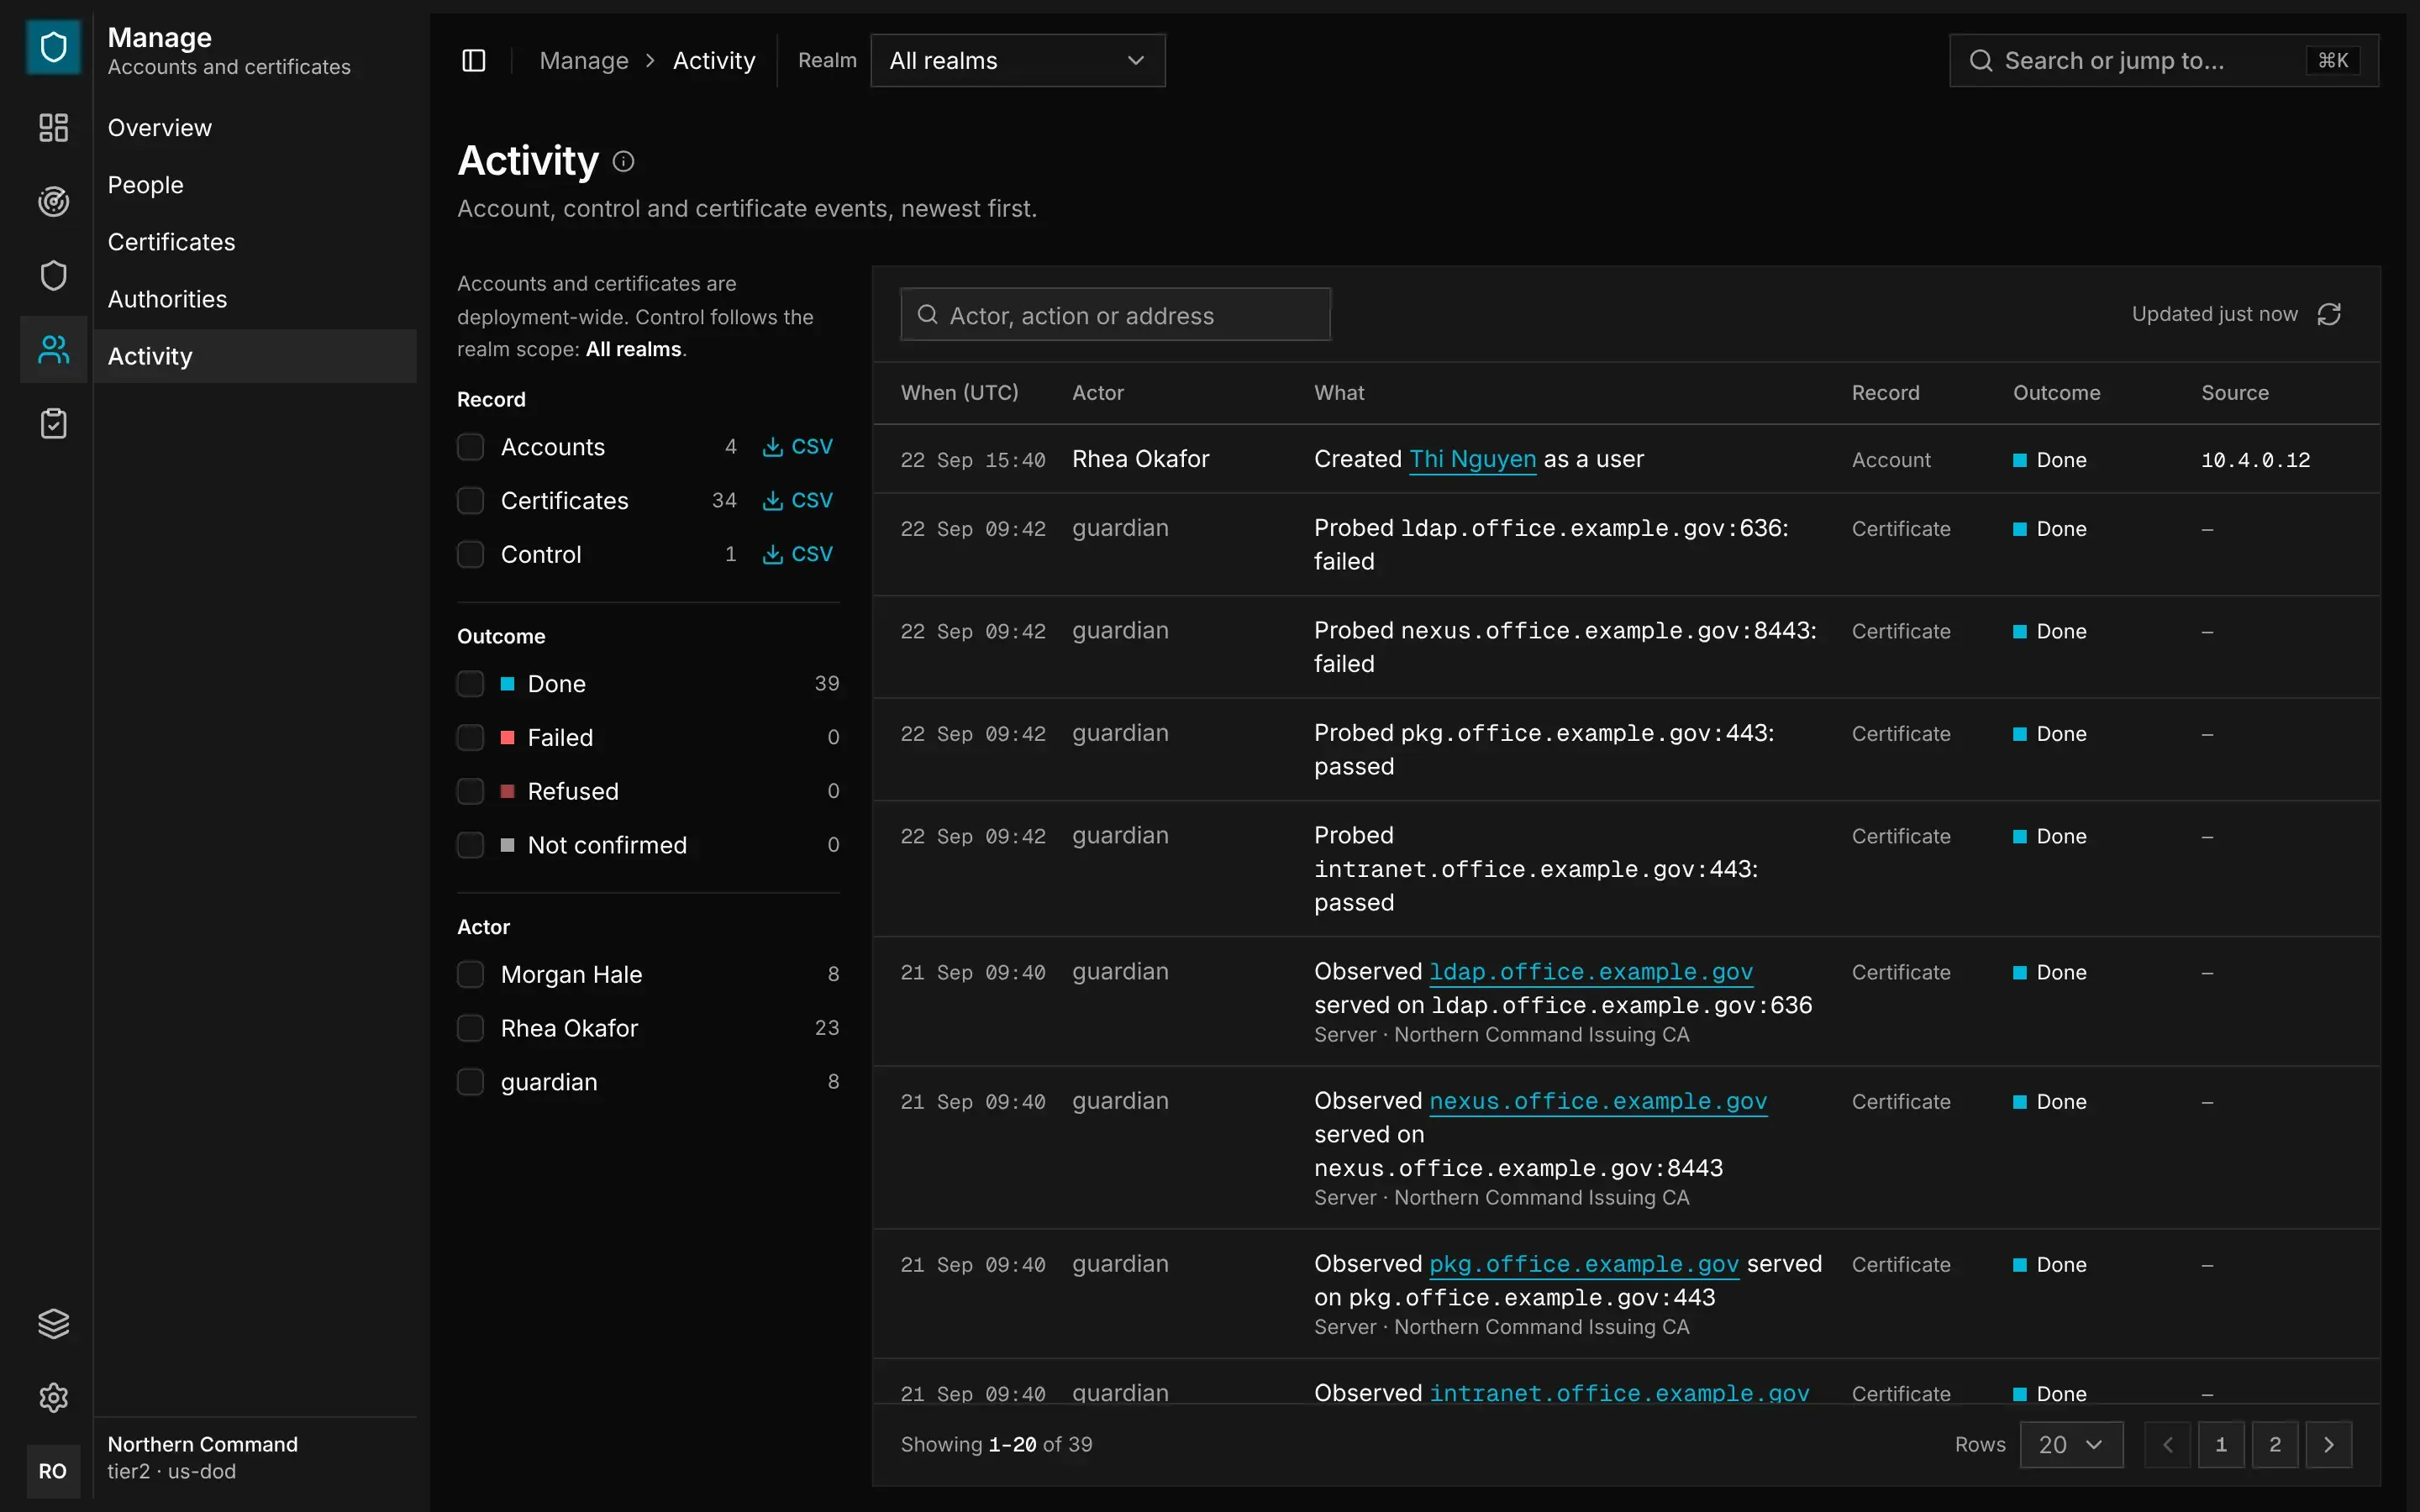
Accounts needing attention, certificates due for renewal, role distribution and the owner of every node and certificate.
Identity, access and certificates.
- Role-based accessFour hierarchical roles: admin, manager, auditor and user. Sign in with one-time codes or your identity provider, with automatic sign-out for idle sessions and lockout after repeated failures.
s.ibarra · locked out · brute-force detection - Clear ownershipEvery node and certificate is linked to the person who commissioned or issued it, so nothing is orphaned when people change roles.
Rhea Okafor · 13 nodes · 16 certificates - Post-quantum PKIYour own root and issuing CAs, ML-DSA from root to leaf. Issue from a signing request so private keys stay where they were generated, renew without re-keying, and revoke with a reason. Revocation lists are published daily.
Northern Command Issuing CA · ML-DSA-65 - Complete audit trailEvery account, certificate and control event, with who made the change and from where. Filter by record, outcome or actor, and export to CSV.
Rhea Okafor · created t.nguyen as a user
Post-quantum TLS and PKI in a single binary.
- ProbeConnect to any TLS server as a FIPS 140-3 client and report the negotiated version, key exchange, signature and certificate chain.
- ServeRun a FIPS 140-3 TLS 1.3 server and report what each client offered and what was negotiated.
- Issue and verifyGenerate ML-DSA keys, signing requests and certificates, run a managed CA with revocation lists, and verify any chain against your own roots.
- FIPS 140-3Every key, signature and cipher comes from the Go Cryptographic Module, and PKCS#12 files use the approved profile.
conflux cert · probing a TLS 1.3 server
conflux cert probe server.example:8443 --ca root.pem --require-pq
Connected to server.example:8443 (192.0.2.10:8443), as server.example
tls TLS 1.3, TLS_AES_128_GCM_SHA256
key exchange
signature
chain verified for server.example, authentication pqc
post-quantum
Ready to take ownership of every identity?
Talk to us about running the guardian on your own infrastructure. Audit then turns its records into the evidence your auditors need.